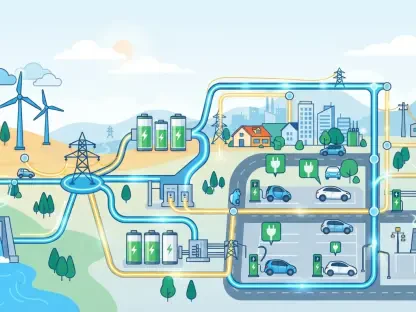
A probabilistic cyber-risk index allows grid defenders to prioritize protection by calculating the likelihood of an attack alongside its potential economic impact. The modernization of the electrical grid has rapidly transformed it into a sophisticated cyber-physical ecosystem through the deep integration of artificial intelligence, the Industrial Internet of Things, and high-speed communication protocols. In 2026, these advancements in smart grids offer unprecedented efficiency and real-time reliability for utility providers and consumers alike. However, this increased connectivity has fundamentally altered the security landscape by blurring the once-clear lines between information technology and operational technology networks. This growing porosity creates an expanded attack surface, leaving critical infrastructure vulnerable to sophisticated digital threats that can cross over from a corporate database to a physical transformer. A critical study conducted by Rajesh Kumar Samala, Mercy Rosalina Kotapuri, and Rama Krishna Kothuri addresses the high-consequence threat of Load Redistribution attacks, a variant of False Data Injection specifically designed to remain invisible to traditional monitoring systems. By manipulating sensor data with high precision, attackers can cause significant operational damage while remaining completely undetected by the baseline security protocols that most utility companies currently have in place.
Advanced Threat Detection and Integrated Pipeline
The Challenge: Invisible Grid Attacks
Traditional security measures often fail to detect load redistribution because they rely on bad-data detection algorithms that primarily flag large deviations from physical laws. In a load redistribution attack, the malicious actor manipulates load measurements across different nodes, or buses, while ensuring the total reported system demand remains constant. Because the sum of the changes equals zero, the grid’s residual-based alarms are never triggered, and the system appears balanced to human operators. Beneath this surface of apparent stability, the underlying data is fraudulent, leading to incorrect power dispatching decisions and transmission congestion. Without a more sophisticated method of detection, these stealthy injections can push a grid toward its physical limits, potentially causing cascading failures and long-term hardware damage. The danger lies in the attacker’s ability to stay within the normal statistical range of the system, making the breach indistinguishable from standard sensor noise or minor fluctuations in consumer demand. Protecting the grid requires a mechanism that can see through this manipulated balance to maintain the actual physical reliability of the network.
A Cohesive: Closed-Loop Defense Framework
The proposed framework moves away from modular, disconnected cybersecurity functions in favor of a cohesive, integrated pipeline where each stage of the security process directly informs the next. This system begins with an adaptive anomaly detector that identifies suspicious patterns and feeds its findings into a probabilistic cyber-risk index. This index then prioritizes a machine-learning engine to identify which specific measurements are most critical to the grid’s current state. By utilizing this holistic approach, the framework creates a dynamic defense that is far more responsive to real-time threats than traditional static protocols. This closed-loop design ensures that as the nature of an attack evolves, the defensive resources shift to compensate, creating a layered shield that covers detection, risk assessment, and active mitigation. This transition to an integrated pipeline is essential for 2026 grid operations, as the speed and complexity of digital incursions have outpaced the ability of human operators to respond to isolated alerts. By automating the connection between detection and resource allocation, the framework minimizes the window of opportunity for an attacker to exploit the lag between a breach and its eventual discovery.
Technical Mechanisms for Risk Assessment
Adaptive Models: Statistical Anomaly Detection
Distinguishing between a coordinated cyberattack and normal daily load fluctuations is one of the most significant challenges for modern grid operators. The study introduces an adaptive statistical model that utilizes a sliding-window approach to recompute statistical benchmarks at every time step, rather than relying on fixed historical means. By avoiding static thresholds that can be easily learned and bypassed by an attacker, the system adapts to natural drifts in power usage, such as those caused by changing weather patterns or the morning ramp-up of industrial activity. This time-varying threshold remains highly sensitive to the sudden, sharp deviations that characterize malicious activity, even when those deviations are mathematically balanced across the network. This sensitivity is crucial for reducing false alarms, which often lead to operator fatigue and the eventual ignoring of legitimate threats. By maintaining a high signal-to-noise ratio, the adaptive model ensures that security personnel only focus on genuine anomalies, providing a more reliable first line of defense that evolves alongside the grid’s operational conditions throughout the day.
Quantifying Vulnerability: Probabilistic Indices
To determine which grid components require the most intensive protection, the researchers developed a reproducible probabilistic cyber-risk index that evaluates three core factors. First, it considers attack probability by combining historical data with real-time AI predictions. Second, it assesses the vulnerability coefficient of specific communication channels and physical buses. Third, and perhaps most importantly, it calculates the potential operational impact of a compromise, measuring the economic loss that would occur if that specific data point were manipulated. By multiplying these factors, the framework generates a prioritized list of measurements, allowing utility providers to focus their limited defensive resources on the areas where a breach would cause the most severe financial and physical harm. This targeted approach is much more cost-effective than attempting to secure every single sensor with maximum encryption, which is often technically impossible due to the sheer scale of the network. The index provides a mathematical foundation for security investments, ensuring that the most critical “vital organs” of the power grid are protected by the strongest possible digital fortifications.
Strategic Resource Management and Security Architecture
Selection Methods: Machine Learning and Strategic Game Theory
Since it is financially and technically impossible to protect every sensor on a large-scale grid, the framework uses gradient-boosted decision trees to identify a critical set of measurements. This supervised machine-learning classifier is trained on vast datasets to recognize which nodes are most attractive to attackers based on their influence over the grid’s economic dispatch. This data-driven selection then informs a game-theoretic model, which treats the interaction between an attacker and a defender as a zero-sum game. By calculating a Nash equilibrium, the system determines a mathematical probability for resource allocation, optimizing the defense strategy to provide the highest level of security for the lowest possible cost. This strategic approach assumes the attacker is intelligent and will always look for the path of least resistance with the highest reward. By using game theory to anticipate these moves, the grid can preemptively harden the specific points that an attacker is most likely to target. This turns cybersecurity from a reactive “whack-a-mole” game into a calculated, proactive defense posture that shifts dynamically as grid conditions and threat profiles evolve.
Operational Security: Zero Trust and Industry Standards
The final defensive layer is a Zero Trust Architecture aligned with IEC 62443 standards, which operates on the principle that no device or user is inherently trustworthy, even if they are located within the network perimeter. The framework implements micro-segmentation, using anomaly scores from the AI detector to constantly re-evaluate the trust level of every device on the network in real time. If a sensor or controller begins to behave unusually, the system can automatically trigger “step-up” authentication requests or completely isolate the device from the rest of the network before it can do further damage. This architecture ensures that even if an attacker successfully steals a credential or compromises a peripheral device, their ability to move laterally through the system is severely restricted. By requiring continuous verification and maintaining strict access controls, the framework minimizes the “blast radius” of any potential breach. This alignment with international industrial standards also ensures that the framework can be integrated into existing utility infrastructure, providing a scalable and standardized solution for the complex security challenges facing the energy sector in the coming years.
Empirical Validation and Future Perspectives
Performance Benchmarks: Accuracy and Mitigation
The validation of the framework was conducted through extensive Monte Carlo simulations on several standard IEEE test systems, including the 14-, 30-, and 57-bus models. The results demonstrated that the AI-driven framework achieved a 97 percent detection accuracy, which was a significant improvement over the 86 percent accuracy found in traditional rule-based detection systems. Beyond just detecting the presence of an intruder, the framework proved remarkably effective at mitigating the actual financial damage caused by load redistribution attacks. It was found that the integrated strategy reduced potential economic losses by 61 percent, whereas static, non-intelligent protection strategies only managed a 27 percent reduction. These figures indicated that by intelligently selecting and protecting only the most critical measurements, operators were able to maintain a high level of resilience without the need for an expensive, full-network overhaul. The simulation data showed that even in complex scenarios with multiple simultaneous points of injection, the probabilistic index correctly identified the high-risk zones, allowing the game-theoretic resource allocator to deploy defensive measures effectively.
Next Steps: Real-World Implementation and AC Modeling
While the simulations provided a strong proof of concept, several critical steps remained for the full-scale deployment of this technology. The researchers noted that future efforts were focused on moving beyond the DC power-flow approximation to address the nonlinear complexities of AC power-flow, which more accurately reflects the physics of real-world grids. Transitioning to hardware-in-the-loop testing was identified as a priority to ensure the framework could handle the inherent latency, signal noise, and communication errors of physical grid controllers. Additionally, there was a clear need to test the system’s performance in environments with high levels of renewable energy, where volatility and uncertainty are significantly higher than in traditional fossil-fuel-based systems. Future work also aimed to incorporate Graph Neural Networks to better understand how the physical topology of the grid influenced attack patterns. By addressing these practical challenges, the research paved the way for a more proactive and intelligent form of cybersecurity. The ultimate goal was to provide a scalable, automated solution that could protect the world’s most vital infrastructure against an increasingly sophisticated and unpredictable landscape of digital threats.